Skip to content
Services_Compliance Services_2000x800px-2-edited

Compliance Services

Implementing IT Compliance in a Structured Manner
Ensure Compliance with Regulatory Requirements

Regulatory requirements are steadily increasing across all industries. The NIS2 Directive covers a significantly larger group of companies than before, including a large portion of small and medium-sized enterprises. In addition, industry-specific requirements such as DORA and MaRisk apply, as well as—for operators of critical infrastructure—the requirements of the KRITIS regulation.

DATAGROUP offers structured compliance services that systematically integrate IT compliance into existing IT services. Compliance is not viewed in isolation but is implemented as an integral part of a holistic operating model.

Your Benefits at a Glance

  • Compliance-ready CORBOX services available for purchase as the foundation for IT compliance
  • Structured compliance services, including reporting and documentation
  • Professional Identity and Access Management to support regulatory requirements
  • Transparency and risk minimization through active license management
  • Support for implementing regulatory requirements such as NIS2

Compliance Reporting for IT Compliance and NIS2 Requirements

Companies subject to regulatory requirements such as NIS2 need verifiable evidence and robust reporting structures. Compliance reporting provides structured reports, attestations, and certificates to demonstrate compliance with regulatory requirements.

In the regulated financial sector, it also enables operations that comply with regulations based on established standards such as MaRisk and DORA. In specialized operational environments, central control and management functions are implemented, including:

Key Features:
  • Establishment of the “Three Lines of Defense” model
  • Integrated management system including risk management and internal control system
  • Documented reporting for IT compliance

Identity and Access Management as the Foundation of Modern IT Compliance

Identity and Access Management (IAM) plays a central role in security-oriented regulations. Structured management of identities and access rights is essential for IT security and IT compliance.

Managed IAM encompasses the automated creation, management, and customization of user accounts, as well as approval-based assignment of permissions. In addition, IAM Consulting provides support for role and permission design, as well as for the implementation of authorization models that meet regulatory requirements.

Key Features:

  • Automated identity and permission management
  • Approval-based access control
  • Support for role and permission design

License Management to Ensure Compliance and Cost Transparency

Complex licensing models increase the risk of violations of license terms. Structured license management reduces compliance risks and provides transparency regarding actual software usage.

The service enables centralized management and monitoring of software licenses, helps optimize licensing costs, and contributes to long-term adherence to IT compliance requirements.

Key Features:
  • Centralized license management and usage analysis
  • Minimization of licensing and audit risks
  • Support for optimizing and planning current and future licensing needs

Talk to us about your project

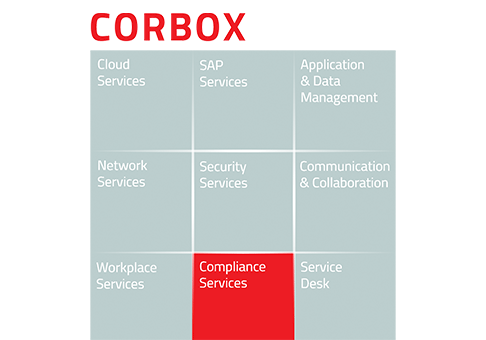
Grafische Darstellung der CORBOX-Service-Bausteine mit hervorgehobener Kategorie „Compliance Services“.

IT Compliance as Part of CORBOX

Compliance services are an integral part of CORBOX, DATAGROUP’s modular IT service portfolio. The individual service families are designed to structurally incorporate regulatory requirements—from infrastructure and security to service desk and cloud.

Companies can combine compliance solutions with other services as needed, thereby creating a consistent foundation for IT compliance, cloud compliance, and data compliance. The services are delivered from German data centers and adhere to certified security and governance standards.
Learn more about Corbox


Compliance Services Client Projects

NRW.Bank_600x350

IT Security and IT Outsourcing for NRW.BANK's Infrastructure

DATAGROUP ensures the secure operation of NRW.BANK’s IT infrastructure and supports compliance with regulatory requirements. Compliance, security, and monitoring services lay the foundation for a resilient and legally compliant IT environment.

Learn more about IT compliance at NRW.BANK

FAQ – Frequently Asked Questions About Our Compliance Services

Are compliance services integrated into existing IT services?

Compliance services can be designed so that regulatory requirements are not viewed in isolation but are integrated into existing IT services. Infrastructure, cloud, security, and workplace services can be delivered in a compliance-ready manner and adhere to uniform governance and security standards. This results in coordinated compliance solutions that enable end-to-end implementation of regulatory requirements and reduce the administrative burden on companies.

What does IT compliance mean in a business context?

IT compliance refers to adherence to legal, regulatory, and internal requirements in IT operations. These include, among others, NIS2, DORA, MaRisk, and industry-specific security requirements.

How do compliance solutions support NIS2 requirements?

Compliance Solutions provide structured reporting and documentation mechanisms that help companies implement and demonstrate compliance with regulatory requirements.

Why is Identity and Access Management relevant to compliance?

IAM ensures transparent and traceable authorization structures. Approval-based access models support compliance with regulatory requirements and reduce security risks.

How does license management help ensure compliance with regulatory requirements?

Structured license management minimizes risks during license audits, provides transparency regarding software usage, and reduces potential violations of license terms.

Get advice now